◎
29 views
Headers, sections, libraries, imports, exports, resources, version, certificate, TLS, .NET, debug, strings, overlay and more.
Static malware triage for Windows
Inspect .exe, .dll and .sys files without running them. PELens shows headers, imports, resources, certificates, .NET metadata and strings, and raises indicators mapped to MITRE ATT&CK.
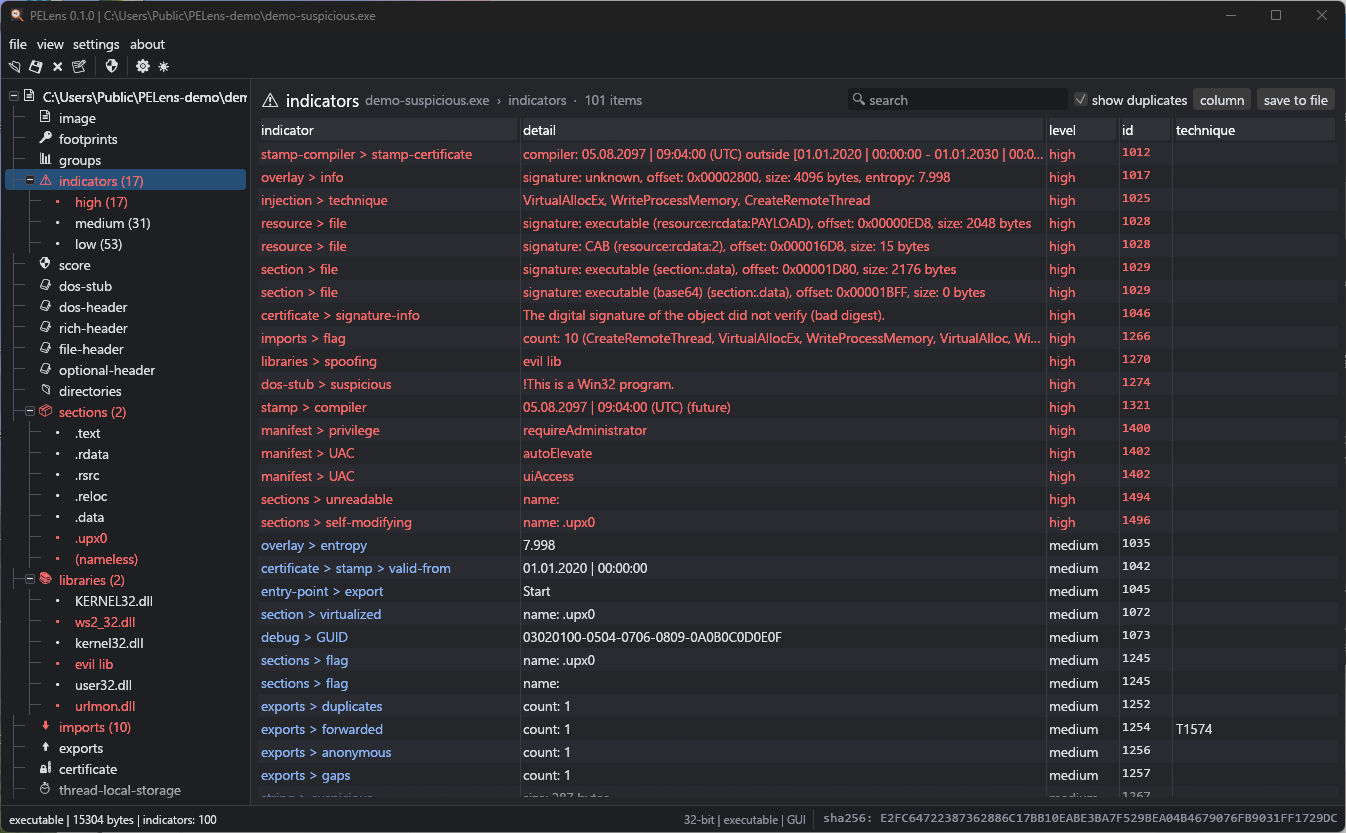
Headers, sections, libraries, imports, exports, resources, version, certificate, TLS, .NET, debug, strings, overlay and more.
142 checks with editable severities, mapped to ATT&CK tactics and techniques: injection APIs, packers, spoofed names, forged stamps, embedded files.
About 2,500 Windows API functions, 900 strings and 100 signatures, written from public sources (CC0). Or point PELens at your own XML knowledge files.
Scan with your rule folders (YARA-X). Matches raise indicators, land in the reports and open in the hex view.
x86/x64 disassembly from the entry point, exports or TLS callbacks, with IAT calls named; every item opens in a fast hex view.
Nothing is executed and nothing is uploaded. VirusTotal lookups send the hash only, with your own key kept in the Windows Credential Manager.
A bounds-checked parser that never panics, fuzzed with libFuzzer, with limits against malformed tables that try to blow up the output.
English, 繁體中文, 简体中文, 日本語, 한국어, Español, Deutsch and Français. Reports in XML, JSON or text from the command line.
Windows 10/11 x64, Linux x86_64, macOS 11 or newer (Apple silicon and Intel). Building from source needs Rust 1.88 or newer.
# verify the download
Get-FileHash PELens-*-windows-x64.zip -Algorithm SHA256

# open a file in the GUI, in Japanese, with the hex view
.\pelens.exe sample.exe -lang:ja -hex

# JSON report with YARA rules and the VirusTotal score
.\pelens-cli.exe -file:sample.exe -format:json -yara:.\rules -vt
# verify the download
shasum -a 256 -c PELens-*.sha256
# open a file in the GUI, in Japanese, with the hex view
./pelens sample.exe -lang:ja -hex
# JSON report with YARA rules and the VirusTotal score
./pelens-cli sample.exe -format:json -yara:./rules -vtPELens is driven by an XML knowledge base. It ships its own open knowledge base, built from public documentation and MITRE ATT&CK, so it works out of the box; with -xml:<dir> it uses other XML knowledge files in the same format instead.
Six Rust crates (parser, knowledge base, analysis, online, CLI, GUI), about 100 tests with over 90 % line coverage in CI, mutation tests and libFuzzer targets for the parser.